


Ultimate Guide to Prepare Free Microsoft SC-300 Exam Questions and Answer
Pass Microsoft SC-300 Tests Engine pdf - All Free Dumps
Microsoft SC-300 exam is a challenging test that requires a deep understanding of Microsoft technologies and their application in identity and access management. SC-300 exam consists of multiple-choice questions, scenario-based questions, and drag-and-drop questions. Candidates must score at least 700 out of 1000 to pass the exam. SC-300 exam is available in several languages, including English, Chinese (Simplified), Japanese, Korean, and Spanish.
How to Register For Exam SC-300: Microsoft Identity and Access Administrator?
NEW QUESTION # 159
You have a Microsoft 365 tenant.
You need to identify users who have leaked credentials. The solution must meet the following requirements.
* Identity sign-Ins by users who ate suspected of having leaked credentials.
* Rag the sign-ins as a high risk event.
* Immediately enforce a control to mitigate the risk, while still allowing the user to access applications.
What should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.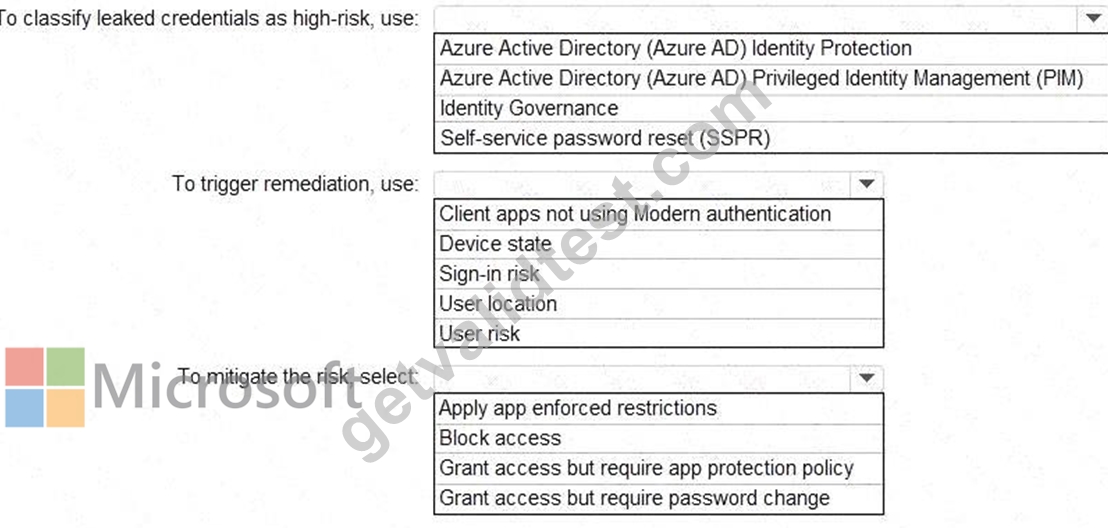
Answer:
Explanation: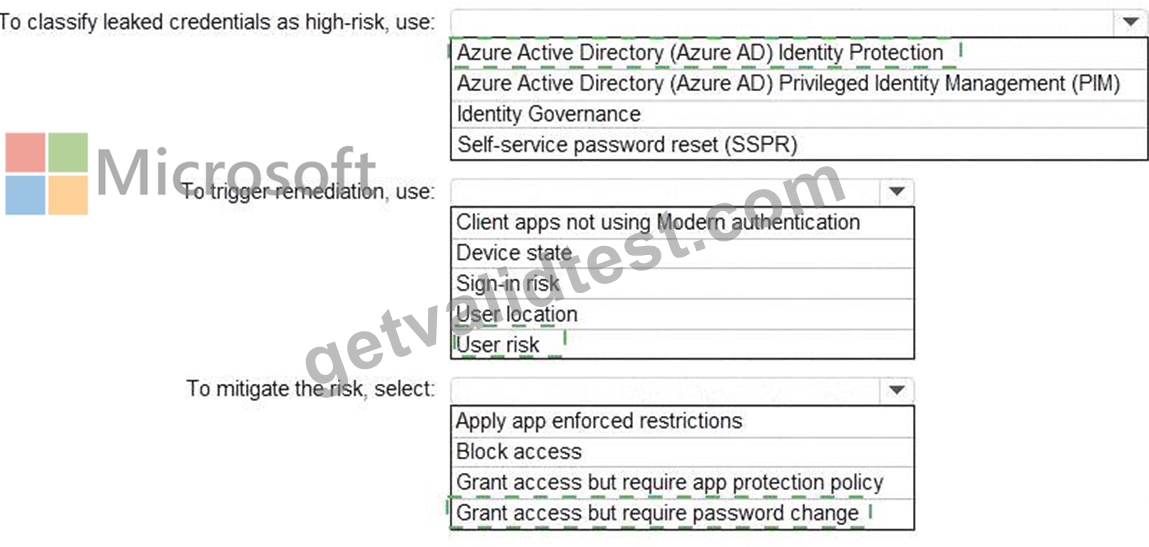
Explanation: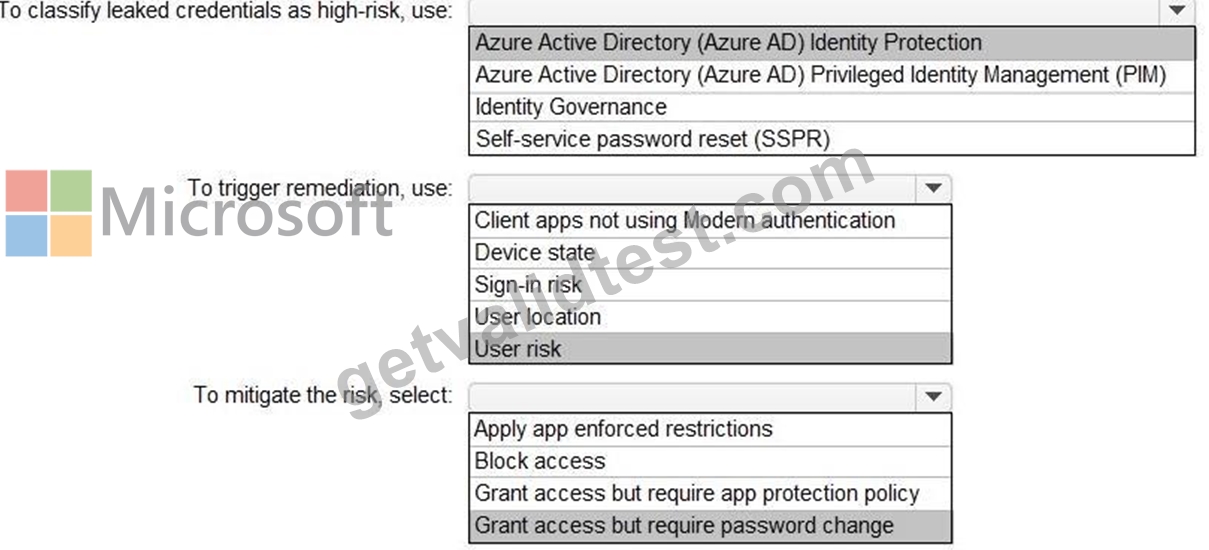
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/concept-identity-protection-risks
NEW QUESTION # 160
SIMULATION
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:[email protected]
Microsoft 365 Password: =1122334455667788
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 99999999
You need to configure Microsoft Entra Identity Protection to meet the following requirements:
- Require multi-factor authentication (MFA) for any sign-ins at the high risk level.
- Apply the configuration to all users except for Mod Administrator.
To complete this task, sign in to the appropriate admin center.
Answer:
Explanation: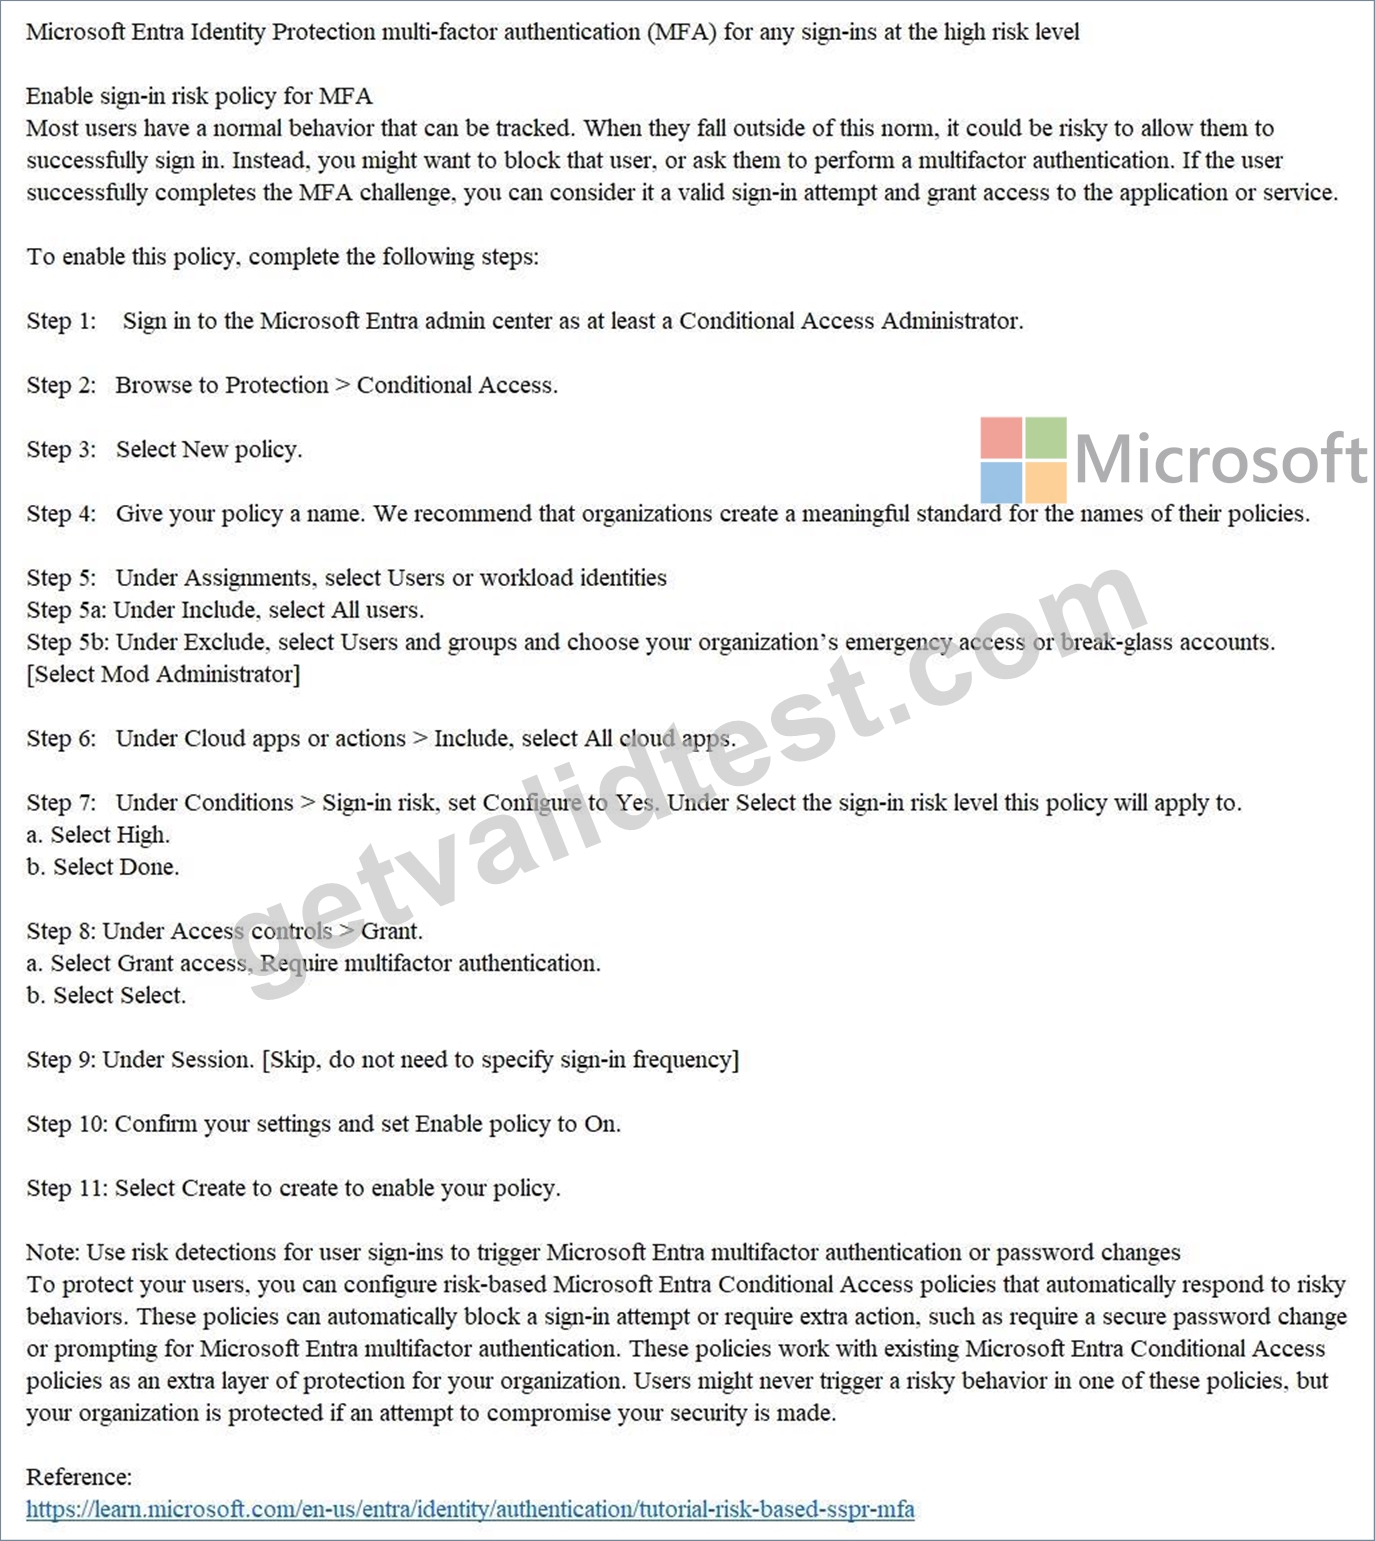
NEW QUESTION # 161
You have a Microsoft 365 E5 subscription that contains a user named User1.
You need to ensure that User1 can create access reviews for Azure AD roles. The solution must use the principle of least privilege.
Which role should you assign to User1?
- A. User Access Administrator
- B. Privileged role administrator
- C. User administrator
- D. Identity Governance Administrator
Answer: C
Explanation:
To create access reviews for Azure resources, you must be assigned to the Owner or the User Access Administrator role for the Azure resources. To create access reviews for Azure AD roles, you must be assigned to the Global Administrator or the Privileged Role Administrator role.
https://learn.microsoft.com/en-us/azure/active-directory/privileged-identity-management/pim- create-roles-and-resource-roles-review#prerequisites
NEW QUESTION # 162
You have a Microsoft 365 E5 subscription.
You need to ensure that users can only access resources in the subscription from a device that has the Global Secure Access client connected.
What should you do first?
- A. Create a remote network.
- B. Enable tagging to enforce tenant restrictions.
- C. Create a named location.
- D. Enable Global Secure Access signaling.
Answer: A
NEW QUESTION # 163
You have an AzureAD tenant that contains the users shown in the following table.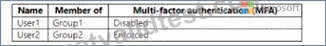
You have the locations shown in the following table.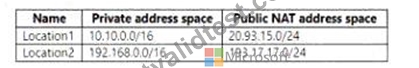
The tenantcontainsa named location that Das the following configurations:
* Name: location1
* Mark as trusted location: Enabled
* IPv4 range: 10.10.0.0/16
MFA has a trusted iPad dress range of 193.17.17.0/24.
You have a Conditional Access policy that has the following settings:
* Name: CAPolicy1
* Assignments
o Users or workload identities: Group 1
o Cloud apps or actions: All cloud apps
* Conditions
* Locations All trusted locations
* Access controls
o Gant
* Grant access: Require multi-factor authentication
Session: 0 controls selected
* Enable policy: On
For each of the following statements select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.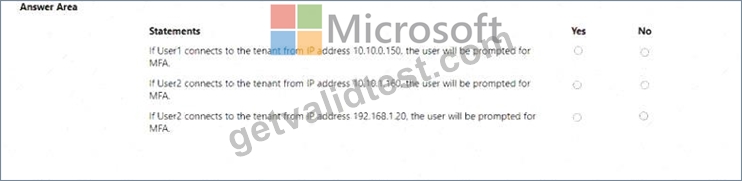
Answer:
Explanation: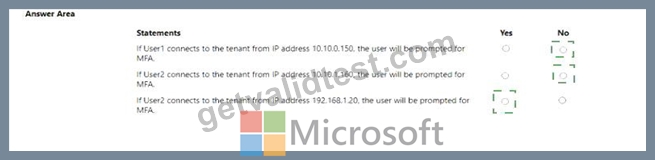
Explanation: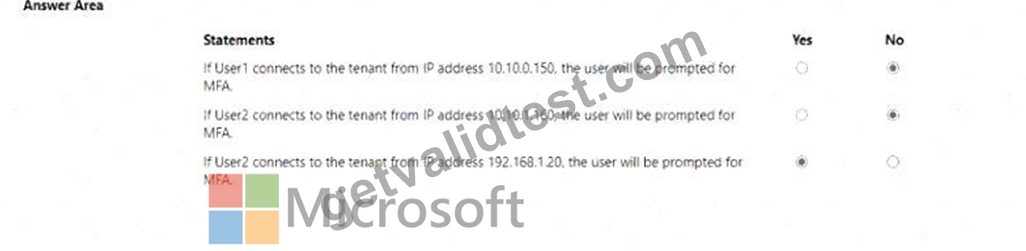
NEW QUESTION # 164
You have an Azure Active Directory (Azure Azure) tenant that contains the objects shown in the following table.
* A device named Device1
* Users named User1, User2, User3, User4, and User5
* Five groups named Group1, Group2, Group3, Ciroup4, and Group5
The groups are configured as shown in the following table.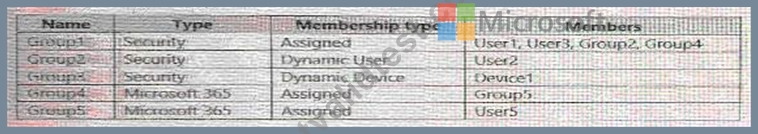
How many licenses are used if you assign the Microsoft Office 365 Enterprise E5 license to Group1?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/enterprise-users/licensing-group-advanced
NEW QUESTION # 165
Hotspot Question
You have a Microsoft 365 tenant and an Active Directory domain named adatum.com.
You deploy Azure AD Connect by using the Express Settings.
You need to configure self-service password reset (SSPR) to meet the following requirements:
- When users reset their password, they must be prompted to respond to
a mobile app notification or answer three predefined security
questions.
- Passwords must be synced between the tenant and the domain regardless of where the password was reset.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.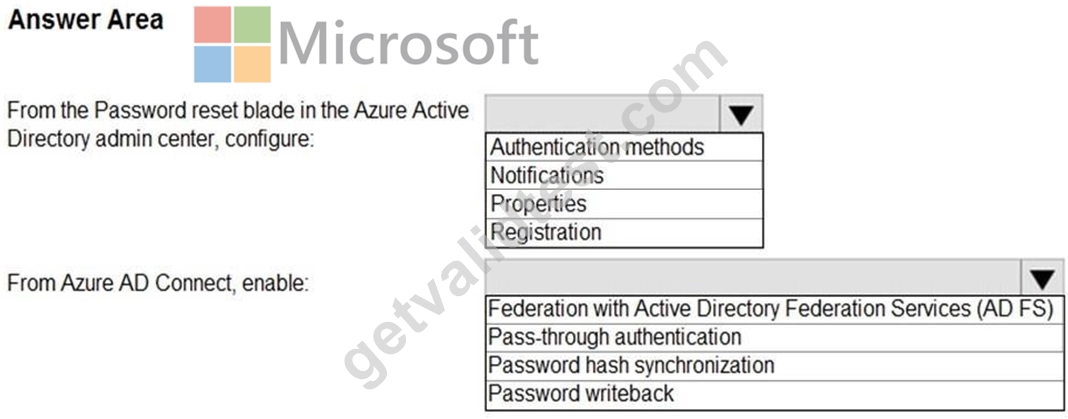
Answer:
Explanation: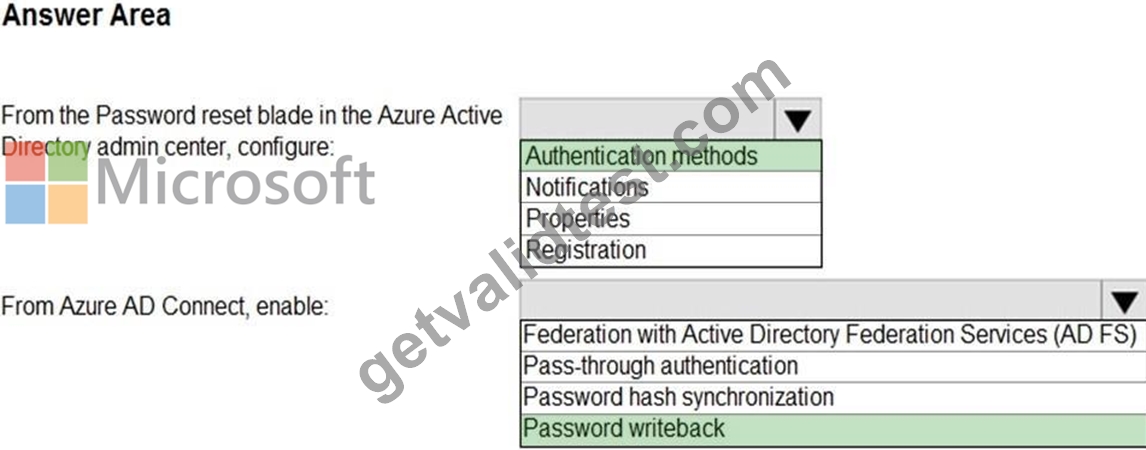
Explanation:
You have Go to Azure active directory > under Manage section Password reset blade > Authentication methods & check the Security Questions In order to sync password between Domain & tenant either you have to do password hash sync & Pass through authentication with password writeback enable in Azure Ad Connect.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-sspr-deployment
https://docs.microsoft.com/en-us/azure/active-directory/authentication/concept-authentication-security-questions
NEW QUESTION # 166
You have an Azure Active Directory (Azure AD) tenant that has the default App registrations settings. The tenant contains the users shown in the following table.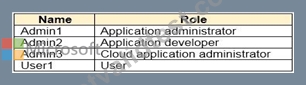
You purchase two cloud apps named App1 and App2. The global administrator registers App1 in Azure AD.
You need to identify who can assign users to App1, and who can register App2 in Azure AD.
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.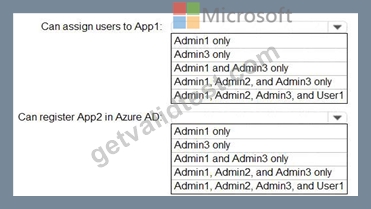
Answer:
Explanation: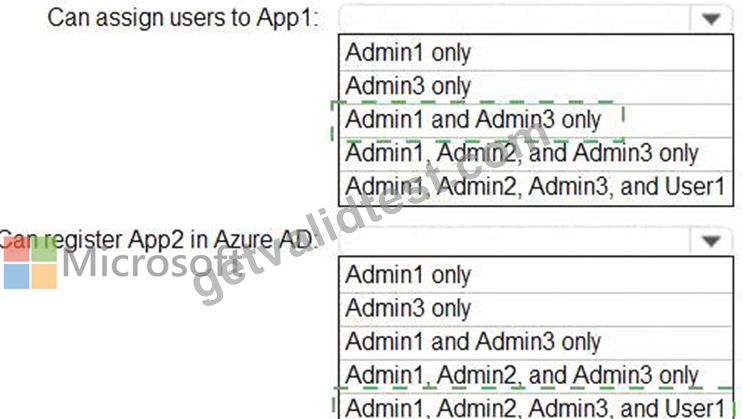
Explanation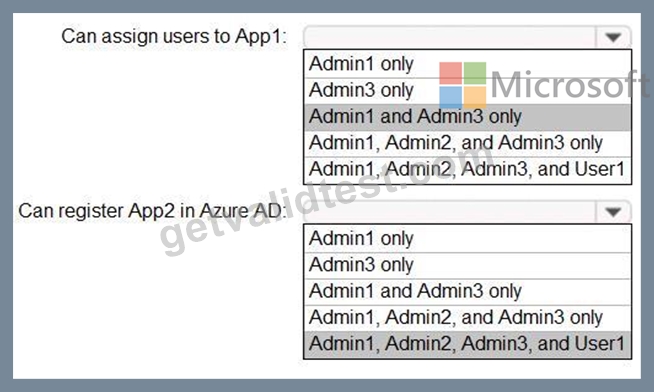
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/manage-apps/add-application-portal-assign-users
https://docs.microsoft.com/en-us/azure/active-directory/develop/active-directory-how-applications-are-added
NEW QUESTION # 167
You have a Microsoft Entra tenant.
You need to query risky user activity for the tenant.
How long will the logs of risky user activity be retained?
- A. 180 days
- B. 60 days
- C. 90 days
- D. 30 days
Answer: C
NEW QUESTION # 168
You have an Azure Active Directory (Azure AD) tenant that has multi-factor authentication (MFA) enabled.
The account lockout settings are configured as shown in the following exhibit.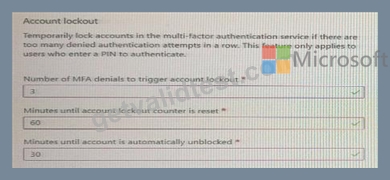
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.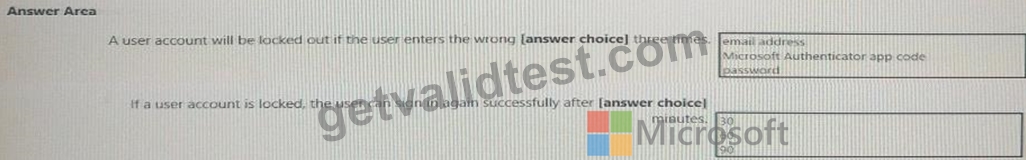
Answer:
Explanation: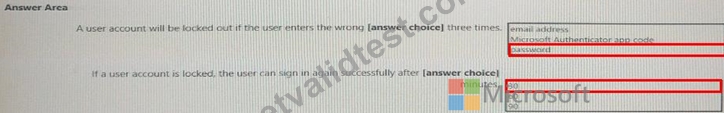
NEW QUESTION # 169
Your network contains an Active Directory forest named contoso.com that is linked to an Azure Active Directory (Azure AD) tenant named contoso.com by using Azure AD Connect.
Attire AD Connect is installed on a server named Server 1.
You deploy a new server named Server? that runs Windows Server 2019.
You need to implement a failover server for Azure AD Connect. The solution must minimize how long it takes to fail over if Server1 fails.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.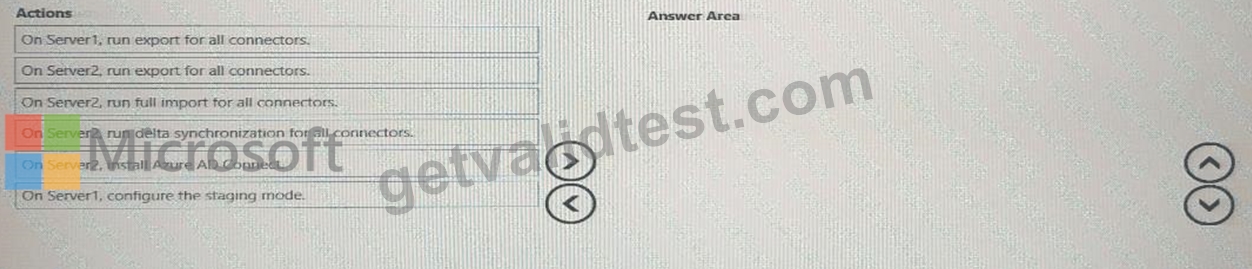
Answer:
Explanation: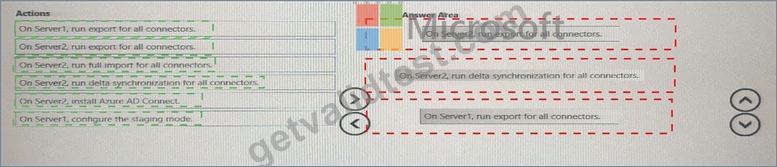
NEW QUESTION # 170
You need to meet the technical requirements for license management by the helpdesk administrators.
What should you create first, and which tool should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.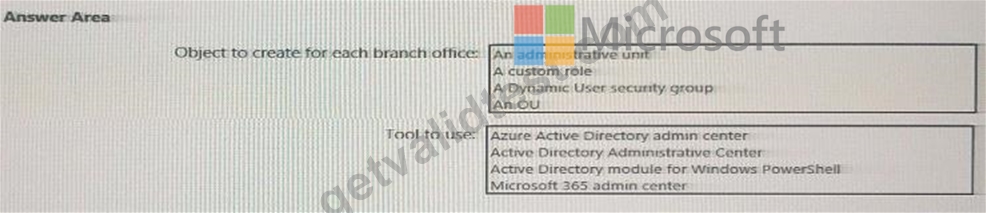
Answer:
Explanation: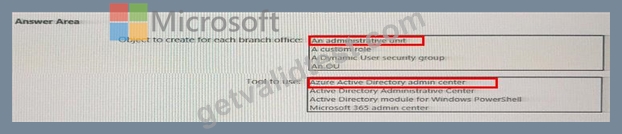
NEW QUESTION # 171
You have an AzureAD tenant that contains the users shown in the following table.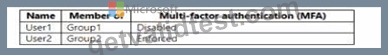
You have the locations shown in the following table.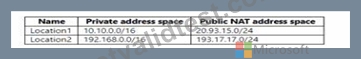
The tenantcontainsa named location that Das the following configurations:
* Name: location1
* Mark as trusted location: Enabled
* IPv4 range: 10.10.0.0/16
MFA has a trusted iPad dress range of 193.17.17.0/24.
You have a Conditional Access policy that has the following settings:
* Name: CAPolicy1
* Assignments
o Users or workload identities: Group 1
o Cloud apps or actions: All cloud apps
* Conditions
* Locations All trusted locations
* Access controls
o Gant
* Grant access: Require multi-factor authentication
Session: 0 controls selected
* Enable policy: On
For each of the following statements select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.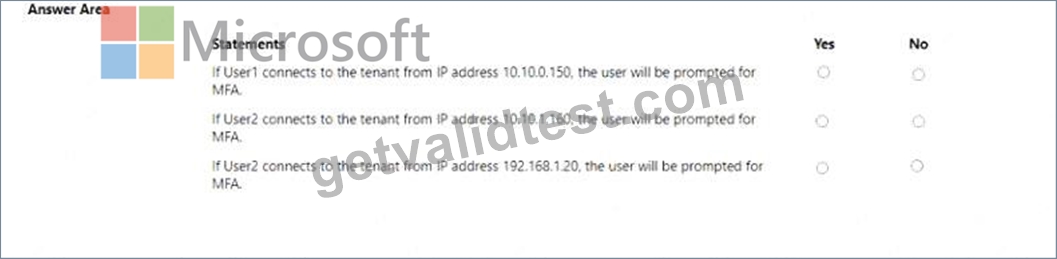
Answer:
Explanation: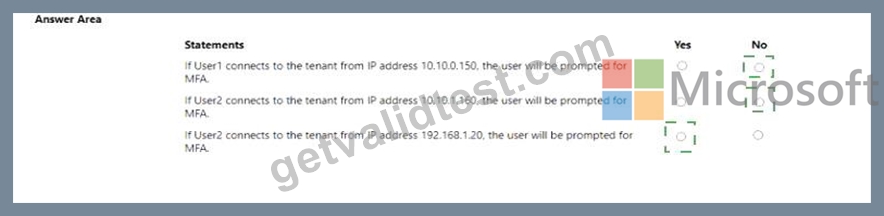
Explanation: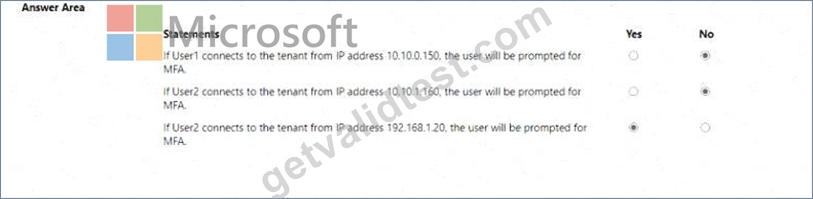
NEW QUESTION # 172
You have a Microsoft 365 tenant.
The Azure Active Directory (Azure AD) tenant syncs to an on-premises Active Directory domain. The domain contains the servers shown in the following table.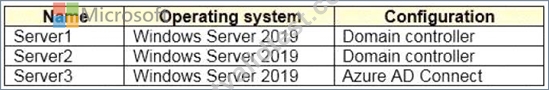
The domain controllers are prevented from communicating to the internet.
You implement Azure AD Password Protection on Server1 and Server2.
You deploy a new server named Server4 that runs Windows Server 2019.
You need to ensure that Azure AD Password Protection will continue to work if a single server fails.
What should you implement on Server4?
- A. Azure AD Connect
- B. Password Change Notification Service (PCNS)
- C. the Azure AD Password Protection proxy service
- D. Azure AD Application Proxy
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-password-ban-bad-on-premisesdep
NEW QUESTION # 173
You have a Microsoft 36S tenant.
You create a named location named HighRiskCountries that contains a list of high-risk countries.
You need to limit the amount of time a user can stay authenticated when connecting from a high-risk country.
What should you configure in a conditional access policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.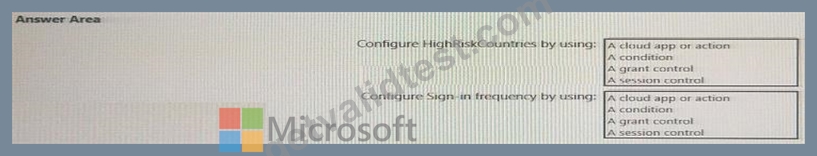
Answer:
Explanation: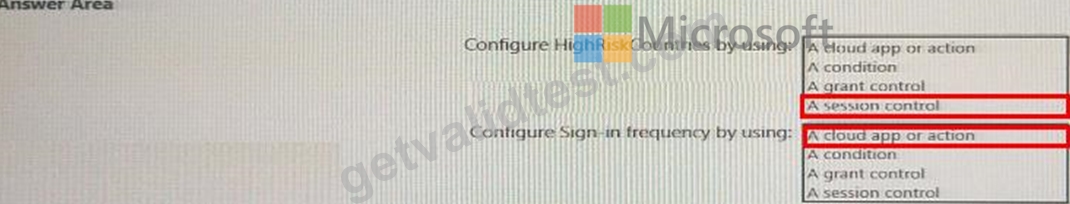
NEW QUESTION # 174
Your company has a Microsoft 365 tenant.
All users have computers that run Windows 10 and are joined to the Azure Active Directory (Azure AD) tenant.
The company subscribes to a third-party cloud service named Service1. Service1 supports Azure AD authentication and authorization based on OAuth. Service1 is published to the Azure AD gallery.
You need to recommend a solution to ensure that the users can connect to Service1 without being prompted for authentication. The solution must ensure that the users can access Service1 only from Azure AD-joined computers. The solution must minimize administrative effort.
What should you recommend for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.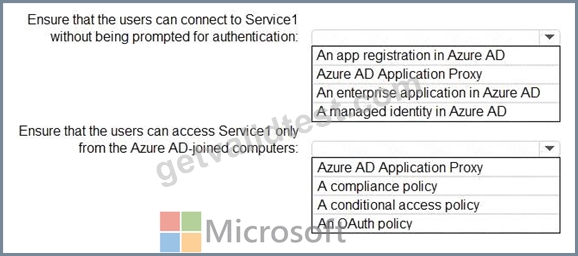
Answer:
Explanation: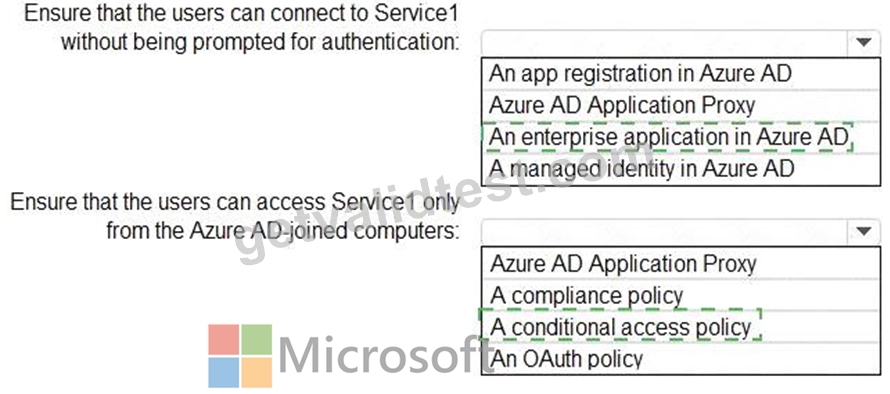
Explanation: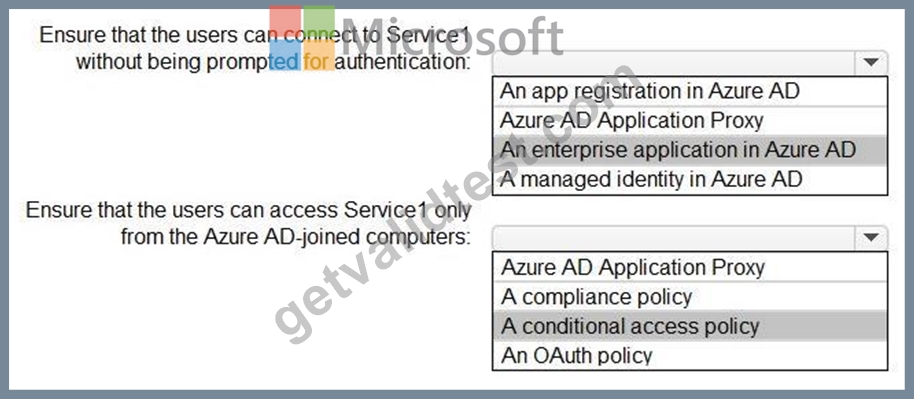
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/develop/active-directory-how-applications-are-added
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/require-managed-devices
NEW QUESTION # 175
......
Online Exam Practice Tests with detailed explanations!: https://troytec.getvalidtest.com/SC-300-brain-dumps.html